Thursday, May 7, 2015

Linux Bash Shell Tutorial : How to change user terminal password in Ubuntu using command line and GUI


 Changing terminal password is an important  part in managing a Linux system. There will be a time when you want to change terminal password to something more secure or reliable. This tutorial will  guide you on how to change user terminal password using either the terminal command or Ubuntu GUI.

1)Change password from the Terminal

1.1) Run in terminal "passwd" command
orca@Positive-Space:~$ passwd                                                                                                                                        


On running the command, you  will be prompted to enter your new password. Enter your new password to confirm. Your password will be updated  straight away .


2)Change password from Ubuntu GUI

2.1) Search user accounts from Ubuntu dash panel
 Search for User accounts setting panel .


2.2)Click  password panel to change the password.


2.3)Change your password and click "Change"


Logout from the system and  test your new password !! :-)

Tuesday, May 5, 2015

How to delete old kernels in Ubuntu using Ubuntu tweak GUI


  Kernel is an important part of Linux system. When you upgrade to new kernel version, the old kernel will be left in your system . As time goes by, this might consume your hard drive and cause  problem to your system.

  One of the examples that old kernel might do to your system is  the system unable to install update from Ubuntu Software updater. When you click "Install Now" button, an error will occur .

"The upgrade needs a total of 79.0M free space on disk '/boot'. Please free at least an additional 7,381k of disk space on '/boot' .Empty your trash and remove temporary packages of former installation using 'sudo apt-get clean' "


  One of the reasons why this problem happens is because the old kernel images are filling up your  /boot drive partition . 

  There are few ways on how to remove old kernel. In this tutorial, I share on how to remove old kernel file images using Ubuntu Tweak program.The guide below will help you to install and delete old kernels using the program

1) Download Ubuntu Tweak program


 1.1)Download Ubuntu Tweak from their website

Downloading Ubuntu Tweak


1.2)Double click the download file and finish the  installation from Ubuntu Software Centre.


Ubuntu Software Centre


2)Run Ubuntu Tweak and delete old kernels

2.1)Search Ubuntu Tweak from Ubuntu dash panel and run the program.


2.2)On the Top side panel click "Janitor" and tick  "Old kernel"  under System.


2.3)Check your latest kernel version from the terminal by typing

orca@Positive-Space:~$ uname -r                                                                          


2.4) Click the  old kernel  that you want to delete and click "clean"  to delete old kernels. It is a good practice to keep  previous latest old kernel version on your system .


Removing unwanted kernel

Remaining kernel


 3)Reboot your system try to update your system again . ;)


Wednesday, April 22, 2015

How to save time doing passive discovery in Kali Linux using discover or backtrack script framework


   Passive discovery is an activity of looking and searching information about certain organization or a network.While Kali Linux has massive tools that we can utilize to do this, it might take us a lot of time in learning each tools.

  To solve this problem, we can use discover scripts or previously known as backtrack scripts in our Kali Linux system.The  framework was written by
Lee Baird .Discover script not only incorporate various kali tools but it is also easy to use .

   In this tutorial I'll share on how to setup the framework with  Kali Linux  and then I will share on how you can use this framework top ook for a network or any network or company passive information.

1)Installing Discover script

 1.1) Clone git to Kali Linux.

orca@omura:~$ cd /opt                                                                                 
orca@omura:/opt$ sudo git clone https://github.com/leebaird/discover.git   


1.2)Setup and install the necessary file for your system .

orca@omura:~$ cd /opt/discover                                                                             
orca@omura:/opt/discover$ sudo  ./setup.sh                                                           


 2 ) Using the framework for passive discovery

2.1) Go to  discover folder and execute the "discover.sh" file .

orca@omura:~$ cd /opt/discover                                                                             
orca@omura:/opt/discover$ sudo  ./setup.sh                                                           


2.2)The framework will load and you will be given a list of  task that can be executed .Use the number in the left for the selection.


Discover framework

2.3)In this example, I will run a script and get information base on domain , I choose "1" .


discover script selection

 2.4)Then Choose "2" and key in the domain name. in this example, i look for information for "www.google.com" .The framework will then run and execute the required tools for this task.


key in the domain url

2.5) Grab a cup of coffee and enjoy it while the scripts doing it's job. :-)


the system is working hard!


2.5) Upon completing,  the result and report will be prepared and you can view it using internet browser.


2.6) To access this file, from the terminal, go  to "/root/data/(domain name)/"

orca@omura:~$ cd /opt/discover                                                                             
orca@omura:/opt/discover$ firefox /root/data/www.google.com                            


Read Next : How to set static IP address and networking details in Kali Linux

Read Previous: How to solve database not connected,cache not built or using slow search in Kali Linux metasploit framework

Thursday, April 16, 2015

Linux Bash Shell Tutorial :How to save terminal session typescript or logfile in Linux


   Sometime as a beginner, intermediate or expert system admin, we need to keep a record on what we did to the system whenever we faced with system problems. One way  we can do this is by recording the Linux terminal session.

 We can save terminal session in Linux by using the built in "script" command.  To record any  terminal session type in script command and followed with the file name that you want.

orca@Positive-Space:~$ script log.01012015                                               

  I make it a habit to include the date in all my logs file name for future reference. Once you entered the command,  the terminal will save everything that you type in the terminal and will save it in current directory location. In this example, "log.01012015" file will be saved in  "user home" directory.

saving terminal session
To stop the terminal saving,you can use exit command .

orca@Positive-Space:~$ exit                                                                     

stopping terminal saving


The saved file can be viewed using any text file editor.

Saturday, January 10, 2015

How to solve database not connected, cache not built or using slow search in Kali Linux Metasploit Framework


  In this tutorial I'm going to share on how to solve database not connected, cache not built or using slow search in Metasploit Framework .


Steps

1) Make sure you are in your Metasploit Framework . Search for any module or exploit in the framework. If your system is using slow search, metasploit will give warning

 "Database not connected, cache not built or using slow search"


Database not connected or cache not built using slow search


2) To solve this problem, you need to rebuild the cache by typing

msf>db_rebuild_cache 


Rebuild the cache
Note: Let the system run and rebuild the system cache for few minutes.

3) After few minutes, try to  search  for any Metasploit module or exploit.If everything went well, you will be able to use fast and quick search in Metasploit Framework.


Saturday, December 27, 2014

How to create a new Postgresql database and new user to work with Metasploit Framework


  In this tutorial, I'm going to share on how to create a new Postgresql database and new user to work with Metasploit Framework .This tutorial might be useful to those who have problems connecting to pre install Metasploit Framework either when you are running on Backtrack or Kali Linux.

In this tutorial,I will create a new database name "msf" and create a user name "msf" with password "metasploit". You will need to use this information when configure "database.yml" file . If you plan to use different database and user name please remember the details

Tutorial rundown

1) Run Postgresql service
2) Create new Postgresql user and database
3) Edit "database.yml" file
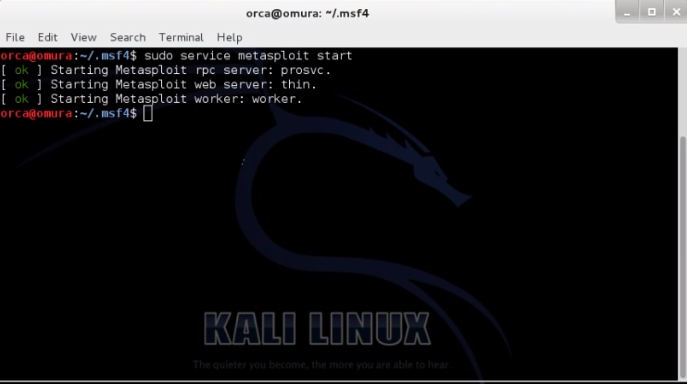
4) Run Metasploit service
5)Run the metasploit framework and check the connected database.


Steps

1) Run Postgresql service by typing

orca@omura:~$sudo service postgresql start


2) Create new Postgresql user and database

2.1) Create new user in Postgresql by login to postgres in root

orca@omura:~$sudo -su postgres
postgres@omura:/home/orca$ createuser msf -P -S -R -D
Enter password for new role :
Enter it again:


2.2) Create new database in Postgresql

postgres@omura:/home/orca$ createdb -o msf msf
postgres@omura:/home/orca$ exit


3) Edit "database.yml" file

3.1) Copy "database.yml" file from /opt/metasploit/apps/pro/ui/config/database.yml to home/.msf4 folder

orca@omura:~$sudo cp /opt/metasploit/apps/pro/ui/config/database.yml  /home/orca/.msf4


NOTE :If you already have database.yml file in /home/.msf4 folder , you can skip this step.


3.2)Change the file permission and edit database.yml file details


orca@omura:~/.msf4$sudo chmod 755 database.yml 


3.3)Edit  "database.yml" file with the information that you use to create user and database.

production:
  adapter :"postgresql"
  database: "msf"
  username: "msf"
  password:"metasploit"
  port:5432
  host: "localhost"
  pool:256
  timeout:5


4) Run Metasploit service

orca@omura:~$sudo service metasploit start 


5)Run the metasploit framework and check the connected database

5.1) Click "Applications>Kali Linux >Top 10 tools> Metasploit Framework "


5.2)Check the connected database

msf> db_status


Saturday, December 13, 2014

How to run metasploit (missing database.yml) and make postgresql,metasploit run at startup


    In this tutorial, I'm going to share on How to run metasploit (missing database.yml) and make Postgresql,Metasploit to run at startup. For official documentation on running Metasploit in Kali Linux, please visit here.


Steps

1) Run postgresql and metasploit service on the machine by typing

orca@omura:~$sudo service postgresql start

orca@omura:~$sudo service metasploit start

Starting postgresql and Metasploit service

2)Run Metasploit framework by going  to Applications>Kali Linux>Top 10 security tools>Metasploit framework

 
Run Metasploit Framework


3) Once Metasploit finished loading, check the database connection by typing
 
msf>db_status


No connected database.

4)If metasploit does not connect to postgresql database, check for "database.yml" file in .msf4 file in home directory


No database.yml file

4.1)Copy database.yml file from opt directory by typing


orca@omura:~$sudo cp /opt/metasploit/apps/pro/ui/config/database.yml /home/orca/.msf4  


Copy file from /opt

4.2) Change file permission by typing

orca@omura:~/.msf4$ sudo chmod 755 database.yml

Change file permission

5)Run Metasploit framework by going  to Applications>Kali Linux>Top 10 security tools>Metasploit framework and check database connection status

Check the database connection
(If it is not connected, you can try to create a new database and new user to make it work with metasploit . I will share in my future tutorial on how to do this)

6)Make postgresql and metasploit service to run at startup by typing

orca@omura:~/.msf4$ sudo update-rc.d postgresql enable

orca@omura:~/.msf4$ sudo update-rc.d metasploit enable


Updating Postgresql and Metasploit service to run at startup

 7)Reboot your machine and try to run Metasploit framework straight after you log on.

System reboot